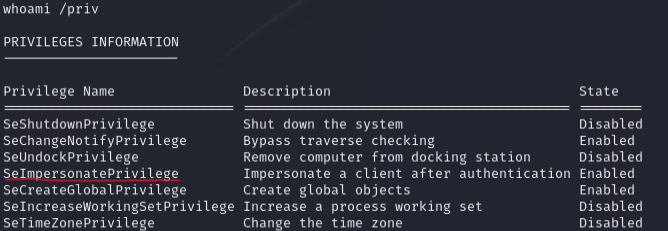
OSCP Quick Hacktricks | Windows: SeImpersonatePrivilege
A piece on how to abuse SeImpersonatePrivilege. A classic in the Windows privilege escalation...

Komorebi—Another Japanese Word that English Needs
Because "sunlight filtering through trees" does not express the same feeling
A Journey of Limited Path Traversal To RCE With $40,000 Bounty!
#Introduce Myself:

4.8 Million Cybersecurity Jobs Are Open. Here's Why You Still Can't Get Hired.
I posted one Level 1 role and got 300 applications. I hired one person. Here's what the talent...

My First Bug Bounty: How I Earned $1,000 With One Simple Step
Bug bounty hunting had been on my radar for a while. After reading dozens of write-ups and diving...
Hacking APIs Series(24/36) — Broken Function Level Authorization (BFLA)
👋Hey security enthusiasts! 🚀
Modern IIS Penetration Testing: A Complete Attacker's Walkthrough
💥 From LFI to RCE via PHP Sessions (PHP 5) — A Complete Guide with Real Examples 🧠💻
By Zoningxtr
How I Turned a Headless Browser into a Critical SSRF Goldmine
Three months. That's how long I stared at bug bounty programs, submitting low-risk findings...
7 "Boring" Micro-SaaS Ideas Making $2k/Month (The Developer's Blueprint)

No AI hype. No complex algos. Just solving rich people's problems.
The "Free" Lie: 12 AI Tools That Are Actually Free (No Trials, No Credit Cards, No Nonsense)
Tired of getting duped by "free" AI tools that aren't? Here's a verified list of...

Open Redirect to XSS: Chaining Vulnerabilities for Maximum Impact
Hello guys! I'm back again with a real-life example of how I turned a simple open redirect...
LFI to RCE: Mastering the Step-by-Step Path from File Inclusion to Full Shell Access
✨ Link for the full article in the first comment
Red Team Automation: 12 Scripts That Save Hours (and Win Real Engagements)
Ever burned a whole weekend on manual recon, only to realize you missed a low-hanging RCE vector...

Exploiting Django CVE‑2025‑64459 on TryHackMe: Complete Walkthrough
How a tiny Django flaw turns simple filters into full‑database leaks.
20 Cache Poisoning Case Study | Depth Analysis of Real-world Bug Reports
An in-depth analysis of real-world cache poisoning vulnerabilities discovered on major platforms,...

5 Advanced Bug Hunting Techniques for Experts (Part -1)
Bug hunting is a critical part of ensuring the security and stability of software systems, and it...
Burp Suite Automation: 12 Custom Extensions That Save Hours for Pentesters and Bug Hunters
Ever spent hours manually fuzzing inputs or hunting for XSS, only to find out you missed a simple...

13.31 Lab: Exploiting XSS to perform CSRF

This lab contains a stored XSS vulnerability in the blog comments function. To solve the lab,...
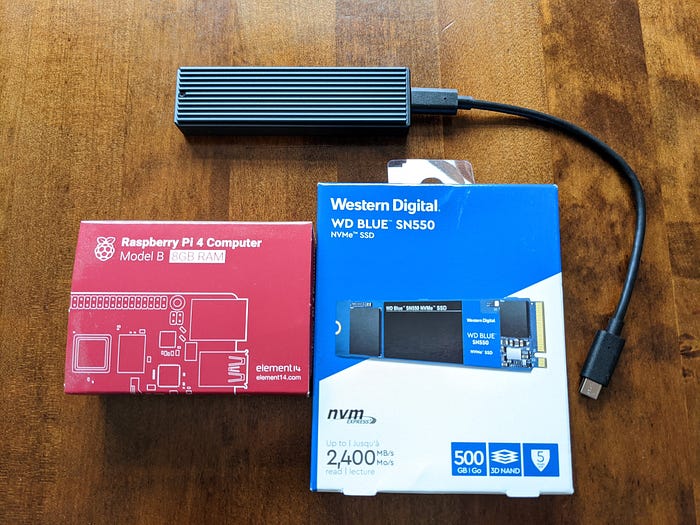
Upgrade your Raspberry Pi 4 with a NVMe boot drive
You can upgrade the storage in your Raspberry Pi 4 with an NVMe drive using USB3 to get more...
Hidden API Endpoints: The Hacker's Secret Weapon 🔍

I'm a cybersecurity enthusiast and the writer behind The Hacker's Log — where I break down...
The Secret Life of Subdomains 🌐: From Takeover to $$$ Bounties
When most people think of a website, they imagine the main domain: example.com. But hackers know...
Internal vs External Pentest: 12 Tools Clients Don't Know Exist (and How Pros Use Them)
Ever sat across from a client, nodding as they ask about "just running Nessus or nmap"...
Stealthy Recon: Master Passive Information Gathering for Pentesters Step-by-Step
✨ Link for the full article in the first comment
Actuator Unleashed: A Guide to Finding and Exploiting Spring Boot Actuator Endpoints
A hands-on walkthrough to find, test and exploit Actuator endpoints for bug hunters.
Top 25 Race Condition Bug Bounty Reports
In this article, we will discuss Race Condition vulnerability, how to find one, and present 25...
Announcing IWCON 2023 Speakers Fourth Batch
Register today to be a part of the coolest Cybersecurity conference and end 2023 on a bang!
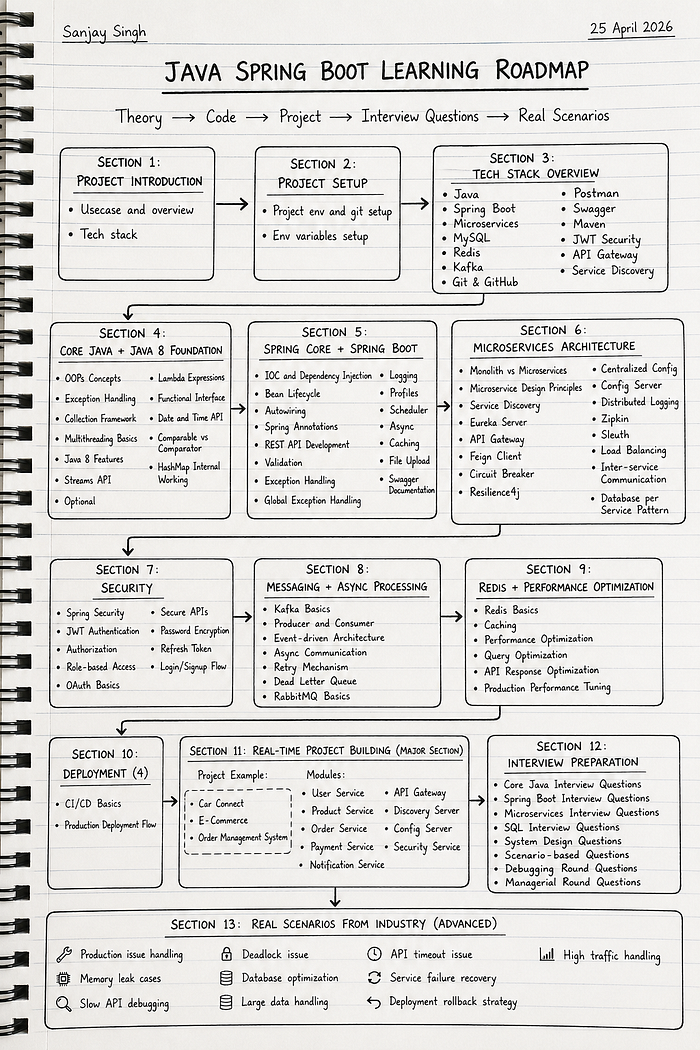
Java Spring Boot Microservices Learning Roadmap (2026)
Theory → Code → Project → Interview Questions → Real Scenarios
Password Reset Flow Testing — The Most Overlooked Account Takeover Vulnerability

Hackers don't always crack passwords. Sometimes they just click "Forgot Password?"...
The-Ultimate-Nuclei-Guide For Hackers In 2026:-
This Scanner That Changed Everything…
Complete Guide to Dnsx for Mass DNS Resolution and Bug Bounty
Essential guide to mass DNS resolution, takeover detection, and sensitive records in bug bounty...
How I Found a $2,800 Bug in 60 minutes — and How You Can Spot It Too
The $2,800 Bug That Took Just 1 Hour to Find
🔍 Power of One-Liners: Master Bug Bounty Automation: 🔍
🚀 Supercharge Your Bug Hunting with Brilliant One-Liners and Crush Vulnerabilities! 🚀
The Top 10 Mistakes Bug Hunters Make and How to Avoid Them
As a bug bounty hunter, finding vulnerabilities in a target application is crucial to success....
Post-Exploitation Toolkit: 25 Commands Every Hacker Uses (Step-by-Step Guide)
✨ Link for the full article in the first comment
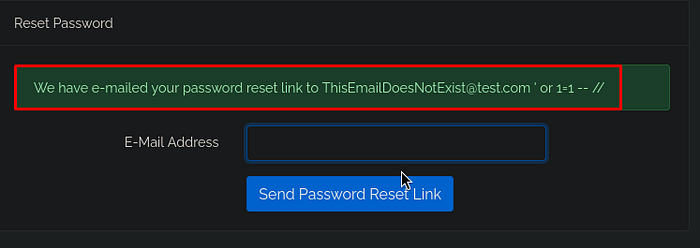
How Boolean-Based Blind SQL Injection Works
Disclaimer

Finding & Exploiting Exposed Google API Keys for Bug $Bounties
Turn exposed Google API keys into real-world impact by accessing Gemini and other Google services...

JS Link Finder Burp Suite Extension Guide
Improve your bug bounty hunting, pentesting, and appsec skills with the JS Link Finder Burp Suite...

Free AI APIs 2026: 39 Battle‑Tested Options For Indie Devs And Creators

Early AI optimism promised openness. Reality in 2026 looks very different.
Cursor AI's Leaked Prompt: 7 Prompt Engineering Tricks for Vibe Coders

Advanced Prompt Engineering Techniques From Cursor's System Prompt
Mastering SQLMap and Ghauri: A Practical Guide to WAF Bypass Techniques
Step-by-Step Methods to Identify, Exploit and Bypass WAF Protections
Prompt Injection Toolkit: 25 Payloads & Techniques for Mastering AI Pentesting
Ever tried breaking an AI chatbot with a 'please ignore all previous instructions' prompt,...
10 Java Basic Concepts Every Developer Should Know (Even Seniors Too)

"Java basics are not basic — they are fundamental."